Practical perspectives on resilience, MDR buying decisions and partner delivery.
Partners3 min read
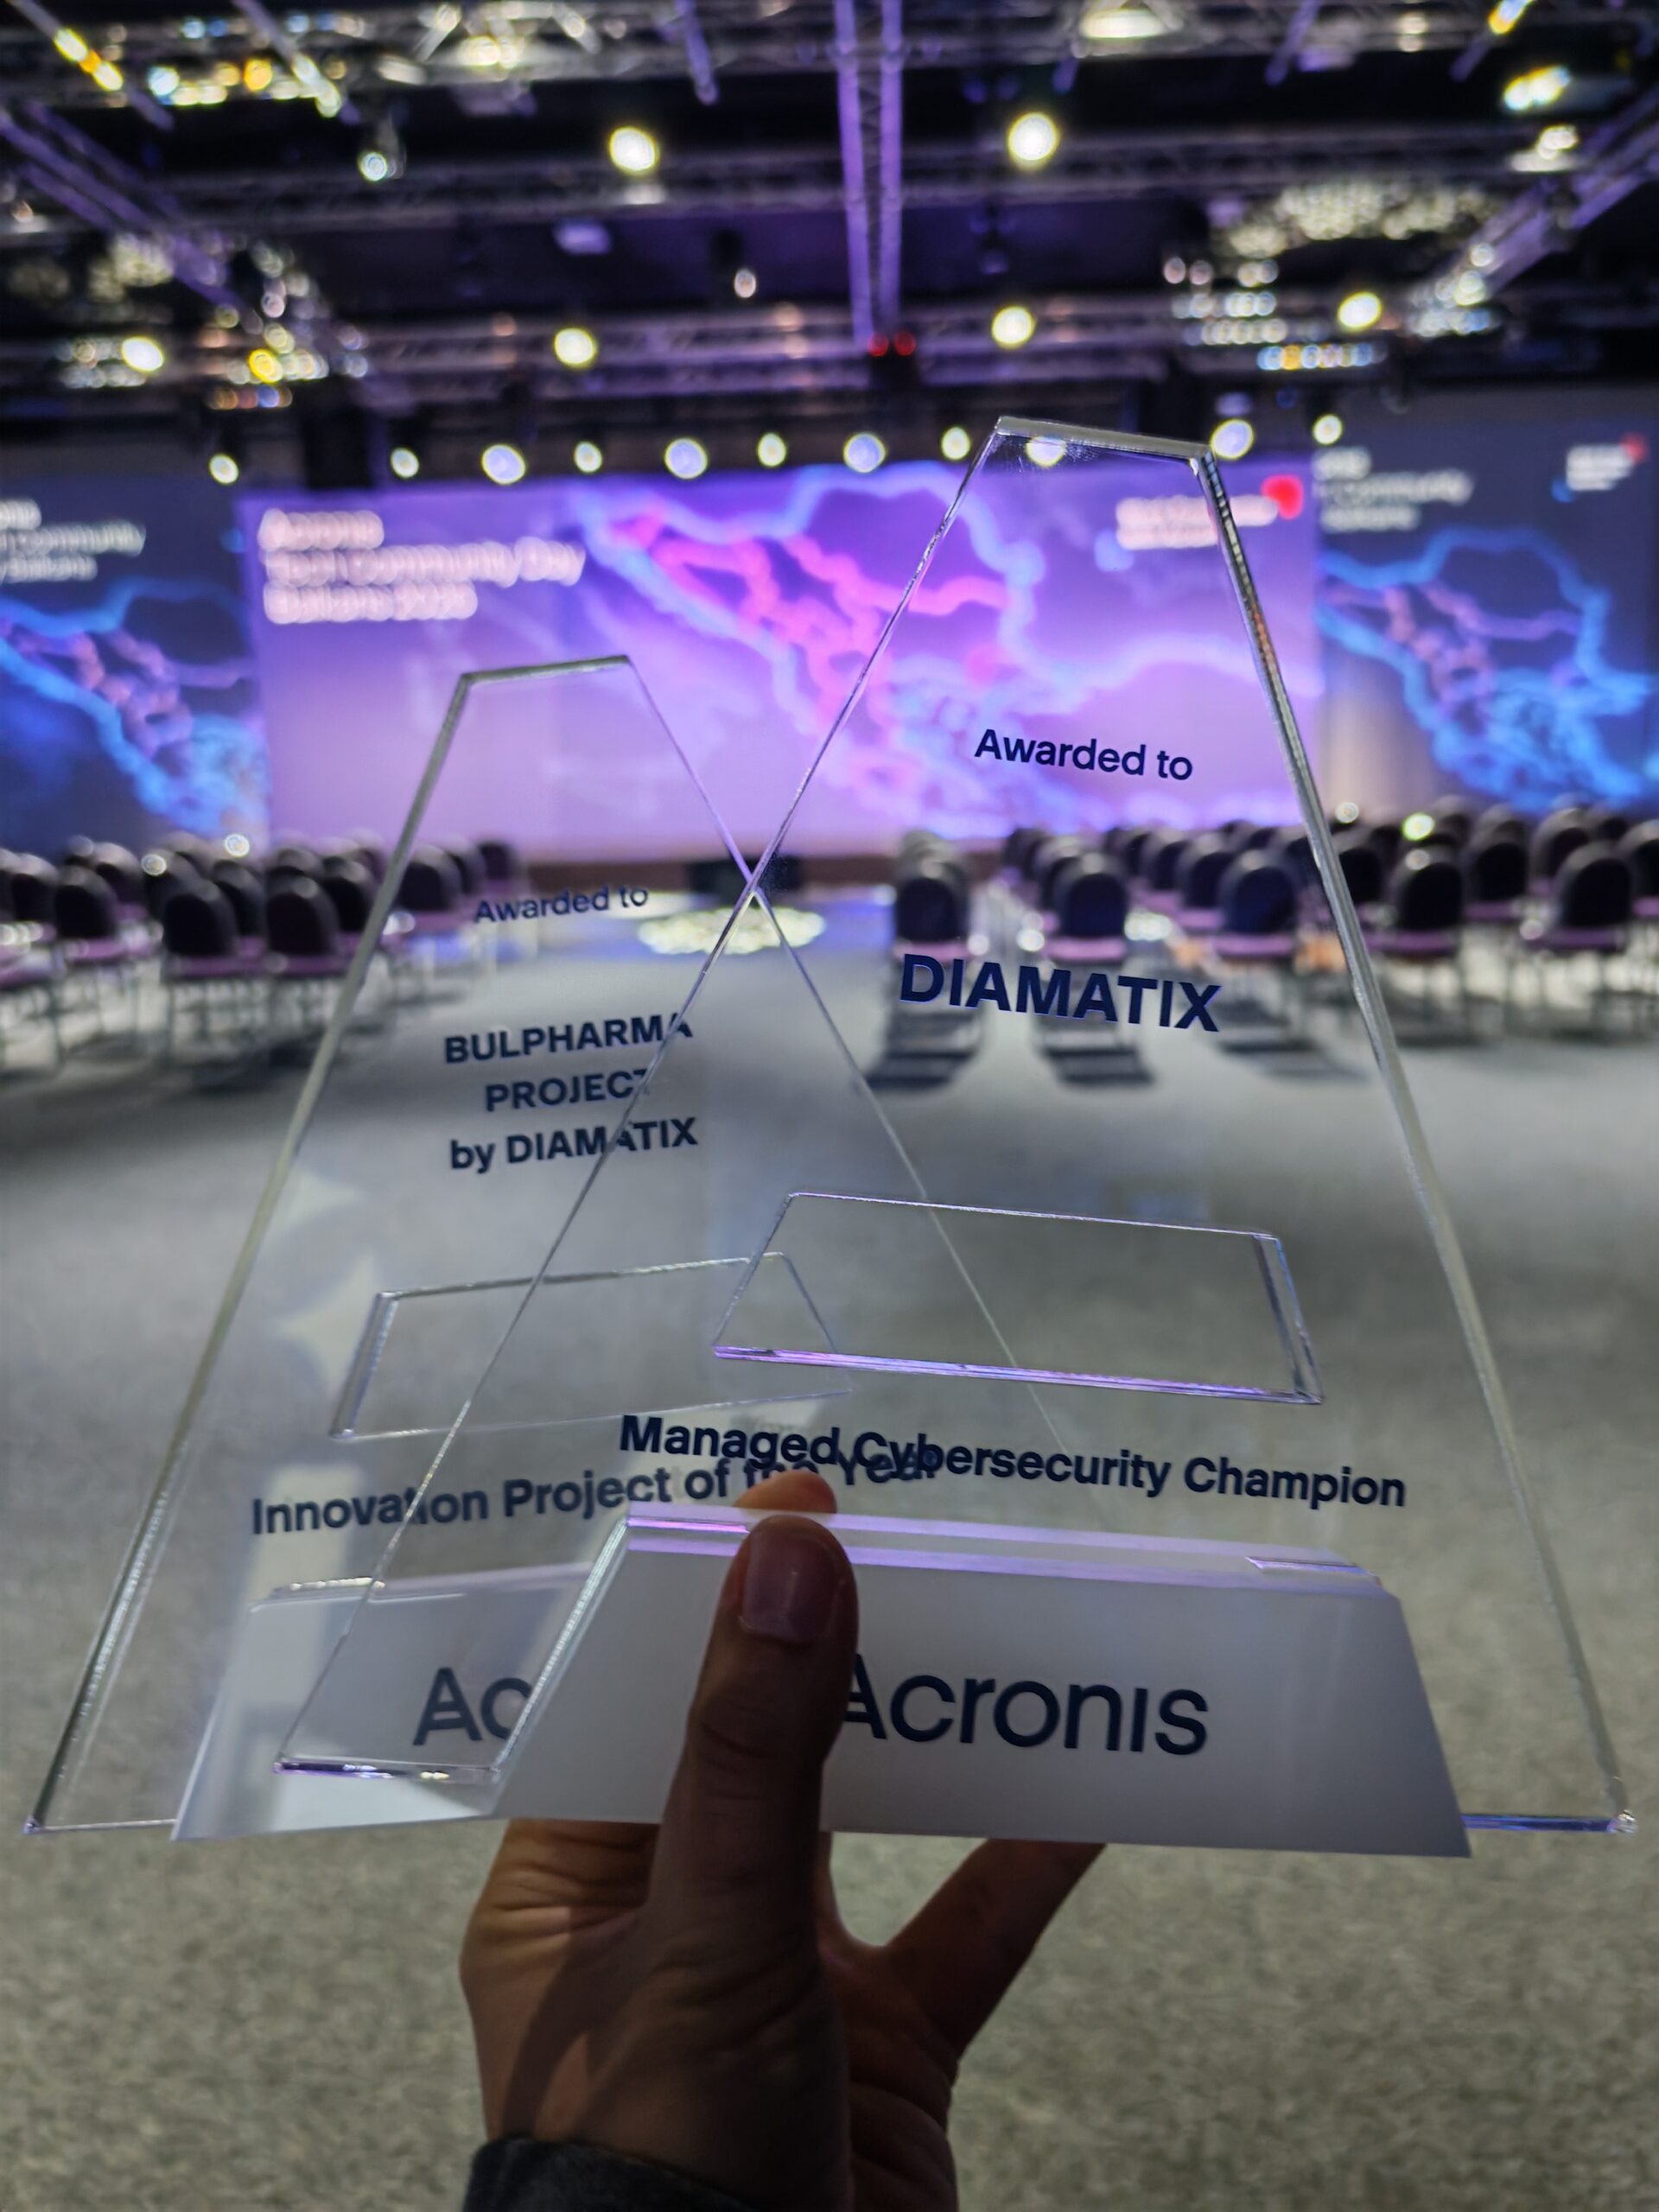
DIAMATIX at Acronis Tech Community Day Balkans 2026: Partnership, Connections and Two Awards
DIAMATIX at Tech Community Day Balkans 2026: Partnership, Expert Exchange and Two Awards 7 October 2026 Tech Community Day Balkans 2026 brought together partners and professionals from across the region DIAMATIX attended Tech Community Day Balkans 2026, organized by Acronis in Sofia. As an…
DIAMATIX at Malta Partner Days 2026: MDR 360°, Partnerships and New Growth Opportunities
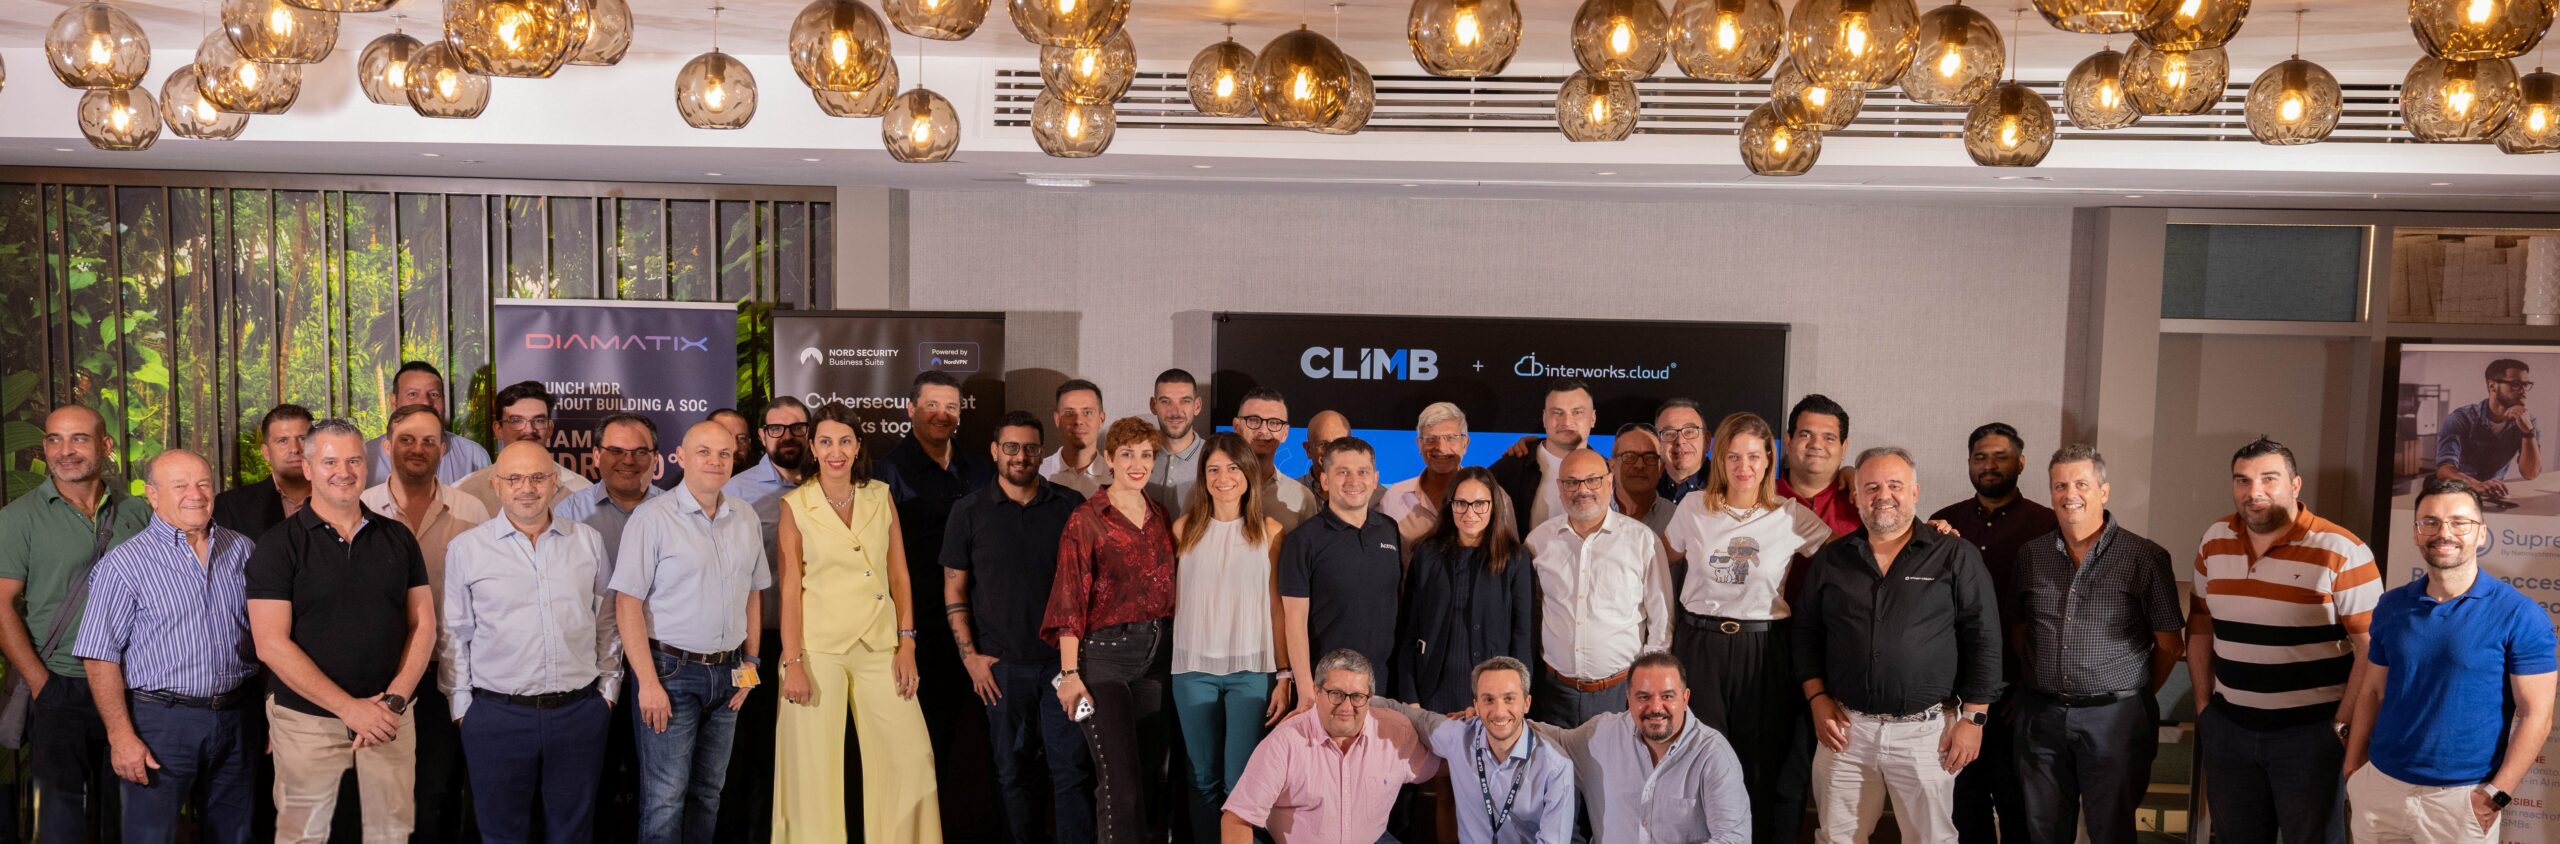
DIAMATIX at Malta Partner Days 2026: MDR 360°, Partnerships and New Growth Opportunities On 6–7 October 2026, DIAMATIX took part in Malta Partner Days 2026, hosted by interworks.cloud at Hyatt Regency Malta. The two-day event brought together MSPs, resellers, technology vendors…
Defining the MDR Service Boundary What is included, where responsibility changes, and what remains outside scope. TL;DR An MDR service boundary defines more than which technologies are monitored. It establishes what the service covers, which activities are performed by the provider,…
LLM SECURITY 101: From AI-Assisted Hacking to AI-Orchestrated Cyberattacks
LLM SECURITY 101: From AI-Assisted Hacking to AI-Orchestrated Cyberattacks When AI Becomes Part of the Attack Workflow In the previous chapter of LLM Security 101, we looked at how AI can accelerate vulnerability discovery and increase pressure on security teams to…
PLAY IT FORWARD 2026: A day on court. An impact beyond.
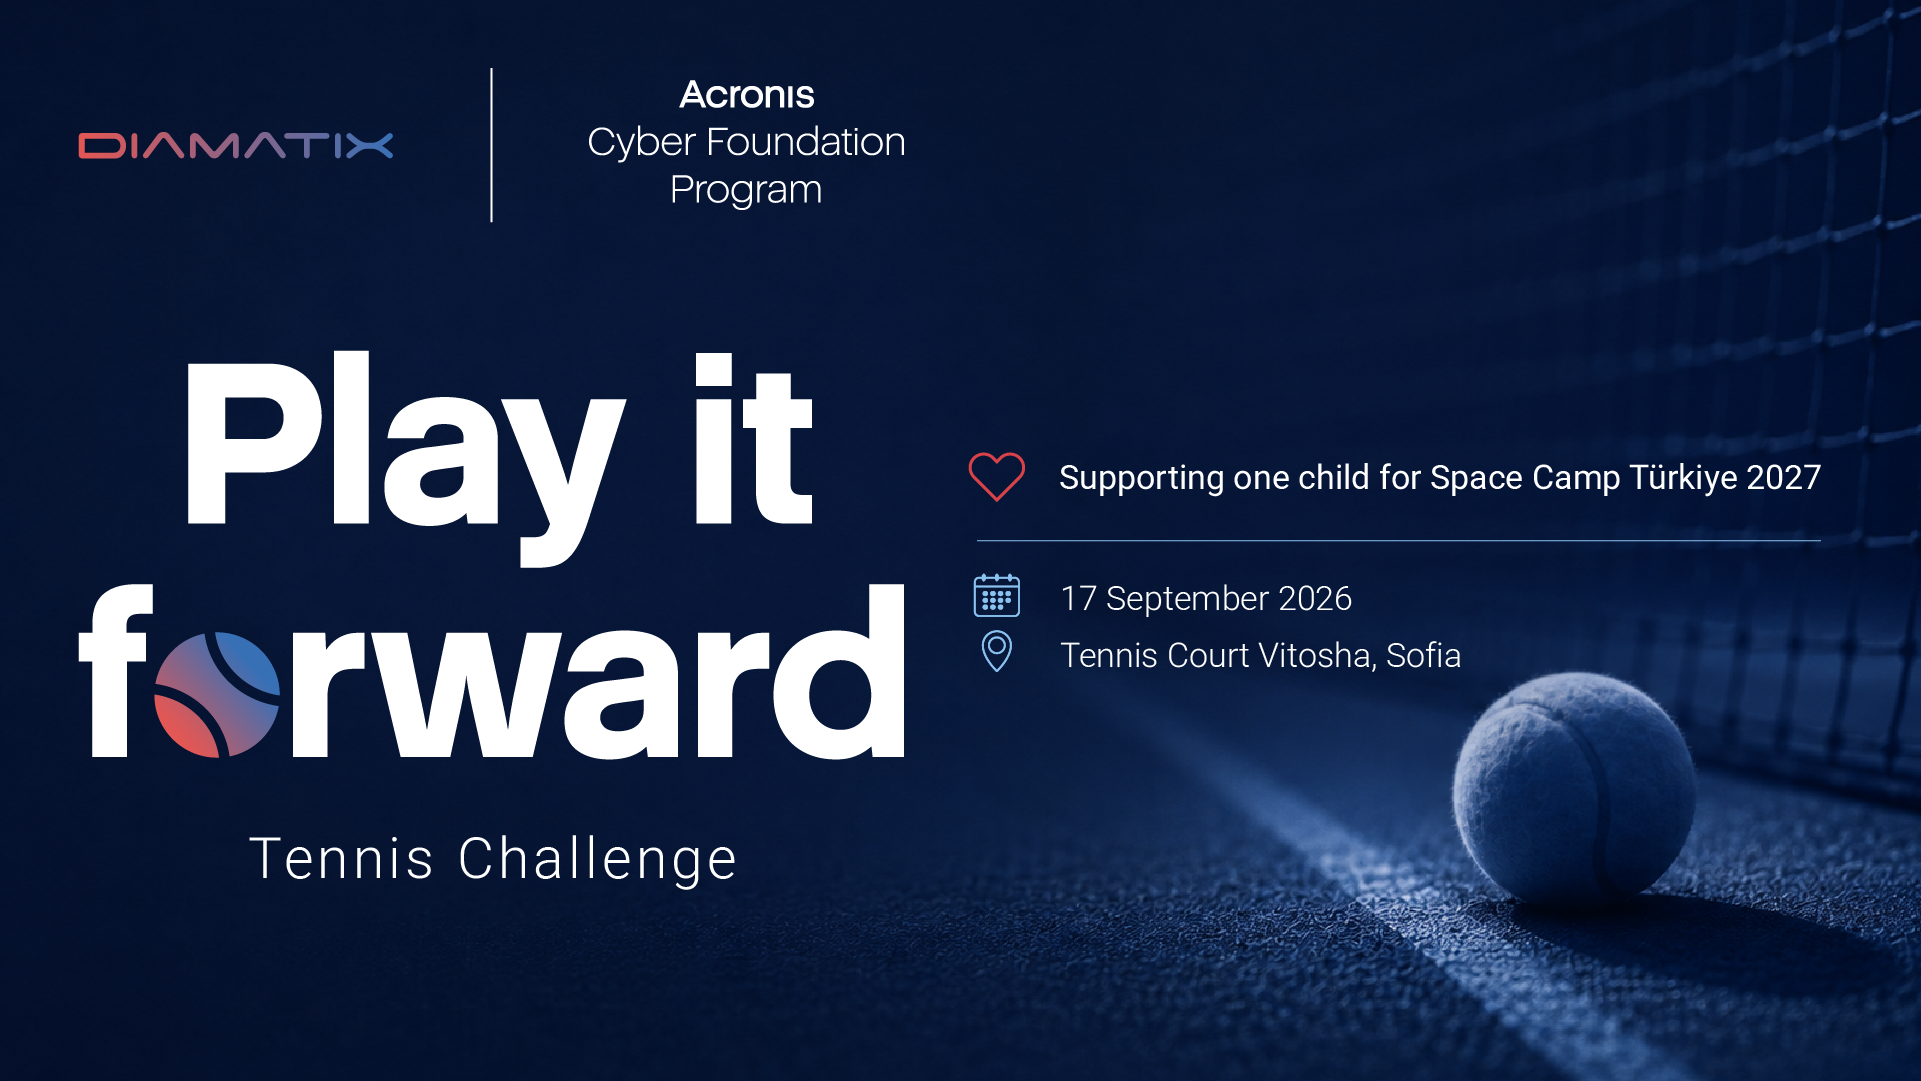
PLAY IT FORWARD 2026: A day on court. An impact beyond. On 17 September 2026, DIAMATIX Community Shield and Acronis Cyber Foundation Program held the first edition of PLAY IT FORWARD, a charity tennis challenge bringing together sport, partnership and a shared cause in Sofia….
DIAMATIX Joins Malta Partner Days 2026 by interworks.cloud
DIAMATIX Joins Malta Partner Days 2026 by interworks.cloud On 6–7 October 2026, DIAMATIX will take part in Malta Partner Days 2026, organized by interworks.cloud at the Regency Ballroom, Hyatt Regency Malta. The two-day partner event will bring together Malta’s IT partner…
LLM SECURITY 101: When AI Finds Vulnerabilities Faster Than Teams Can Fix Them
LLM SECURITY 101: When AI Finds Vulnerabilities Faster Than Teams Can Fix Them The New Pressure on Vulnerability Management The LLM Security 101 series began with the fundamentals: how Large Language Models (LLMs) work, the risks they introduce into everyday workflows,…
PLAY IT FORWARD: DIAMATIX and Acronis Bring Tennis and Purpose Together for Space Camp Türkiye 2027
PLAY IT FORWARD: DIAMATIX and Acronis Cyber Foundation Program Bring Tennis and Purpose Together for Space Camp Türkiye 2027 DIAMATIX and Acronis Cyber Foundation Program are organizing PLAY IT FORWARD, a charity tennis challenge taking place on 17 September 2026 in…
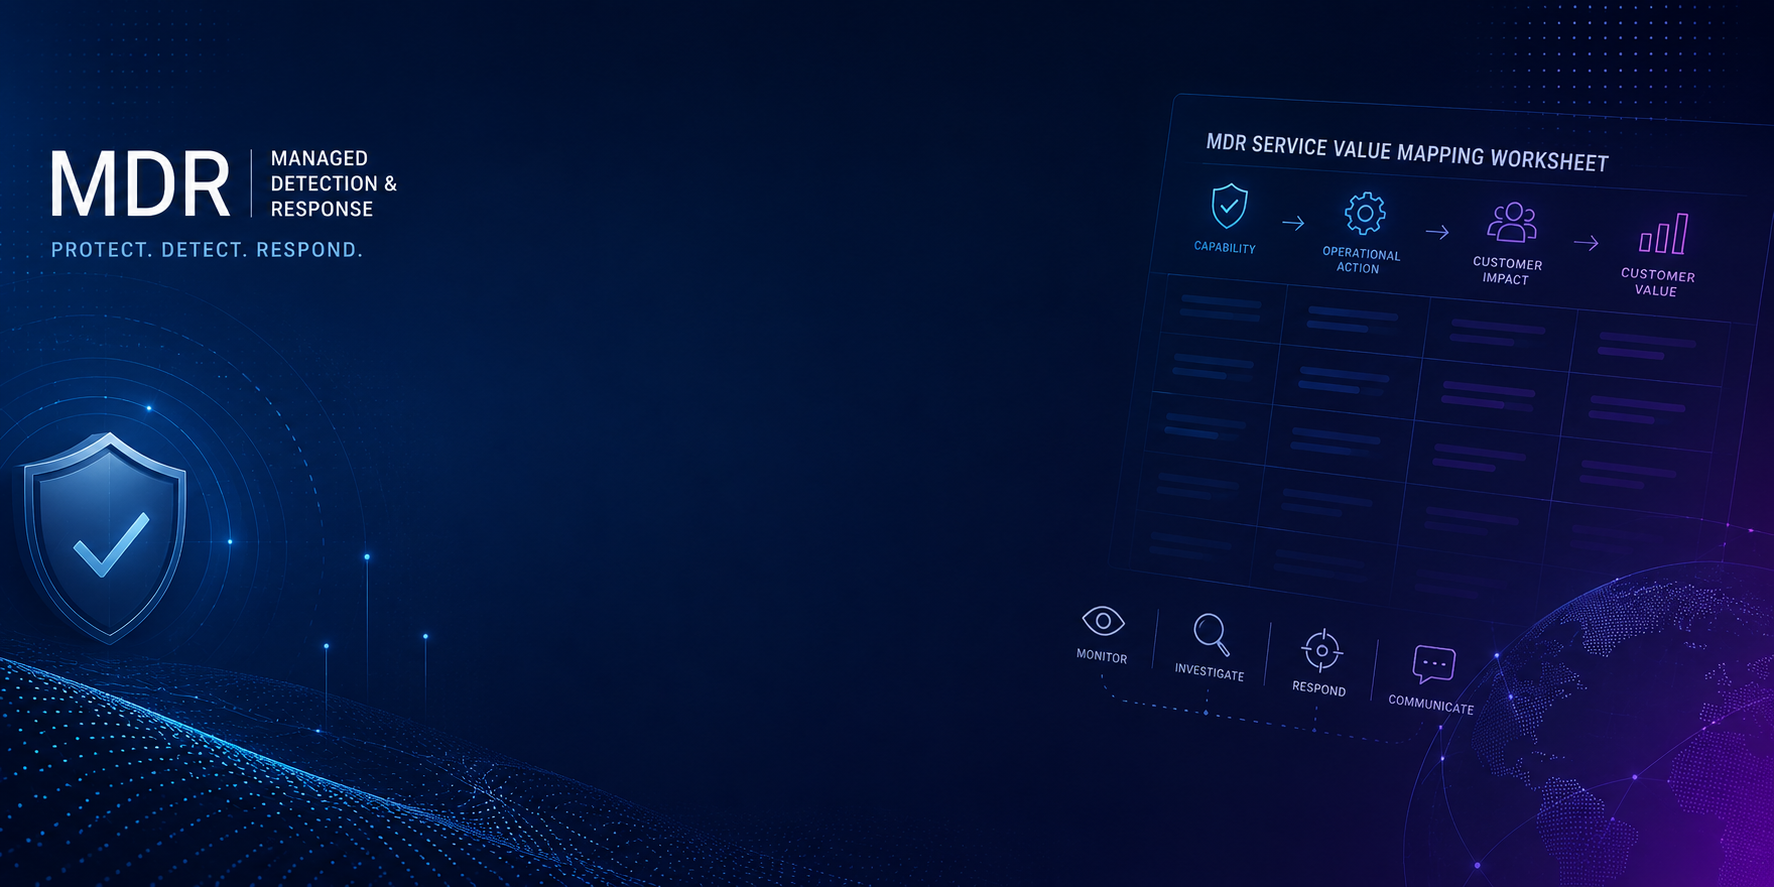
MDR Service Value Mapping Worksheet MDR services are easier to explain and evaluate when technical capabilities are connected to clear operational actions and customer outcomes. The MDR Service Value Mapping Worksheet gives Managed Service Providers (MSPs) a simple framework for mapping…
BlackSeaRama Trophy 2026 Powered by DIAMATIX Marks Its Biggest Edition Yet
BlackSeaRama Trophy 2026 Powered by DIAMATIX Marks Its Biggest Edition Yet 31 August 2026 The BlackSeaRama Trophy 2026 powered by DIAMATIX brought two days of competitive tennis, close matches and strong sportsmanship to the courts at BlackSeaRama Golf & Villas on…
Operational Resilience Framework: How Business Continuity, Recovery, and Security Operations Work Together
Operational Resilience Framework: How Business Continuity, Recovery, and Security Operations Work Together TL;DR Operational resilience is not built through a single technology, process, or team. It depends on several capabilities working together: Business Impact Analysis (BIA) identifies critical services and recovery…
How Shor and Grover Change Cryptographic Risk: A Practical Quantum Demonstration
How Shor and Grover Change Cryptographic Risk: A Practical Quantum Demonstration Quantum computing is often discussed through future scenarios: what might happen when sufficiently powerful quantum computers become available, which algorithms may become vulnerable, and when organizations should begin preparing. A…
What Clients Need to Understand About MDR TL;DR Managed Detection and Response (MDR) should give customers a clear understanding of what is covered, how incidents are investigated, which response actions are available, when customer approval is required, and how responsibilities are…
From MDR Capability to Customer Value TL;DR Managed Detection and Response (MDR) combines technology, security expertise, investigation, and active response. For a Managed Service Provider (MSP), however, listing these capabilities does not automatically explain the value of the service to the…
Post-Quantum Cryptography: Why Preparation Needs to Start Now
Post-Quantum Cryptography: Why Preparation Needs to Start Now Quantum computers are not yet capable of compromising the cryptography that protects modern communications, digital signatures, and key exchange at scale. That does not mean organizations should wait for a sufficiently powerful quantum…
BlackSeaRama Tennis Trophy ’26 Returns on 29 August
BlackSeaRama Tennis Trophy ’26 Returns on 29 August On 29 August 2026, BlackSeaRama Golf & Villas will host the BlackSeaRama Tennis Trophy ’26, bringing tennis enthusiasts together for a day of competition, sportsmanship, and a great atmosphere by the sea. The…
Navigate the MSP Insights & Resource Library Find the articles and practical resources most relevant to your current operational priorities. Building a managed security practice requires more than selecting technologies. Managed Service Providers (MSPs) need an operating model that defines how…
Operational Resilience Readiness Checklist: Evaluate Your Organization’s Preparedness Is your organization ready to maintain critical operations when disruption occurs? Most organizations have implemented at least some elements of operational resilience—backup systems, security monitoring, incident response procedures, or business continuity plans. But…
MSP Insights What Operationally Mature MSPs Have in Common Operational maturity is not defined by the number of tools an MSP uses. It is defined by how consistently the service performs when an alert becomes a real incident. Two providers may…
MSP Service Delivery Maturity Assessment Managed security services are often evaluated by the technologies they use. Operational maturity is what determines how consistently those technologies are translated into effective service delivery. This assessment provides a practical framework for evaluating the operational…
MSP Insights The Service Begins After the Alert TL;DR Generating an alert is only the starting point of a managed security service. The real service begins when security teams investigate the event, determine its business context, decide on the appropriate response,…
Monitoring Is a Capability. Response Is a Service.
MSP Insights Monitoring Is a Capability. Response Is a Service. TL;DR Monitoring is a technical capability. It provides visibility into customer environments and helps identify suspicious activity. A managed security service goes further. It combines monitoring with investigation, decision-making, communication, and…
Disaster Recovery (DR) Testing: If Recovery Was Never Tested, It Does Not Exist
Disaster Recovery Testing: If Recovery Was Never Tested, It Does Not Exist TL;DR Many organizations have backup systems, disaster recovery procedures, and recovery environments. Far fewer have proven that these capabilities actually work under real conditions. Disaster recovery testing validates whether…
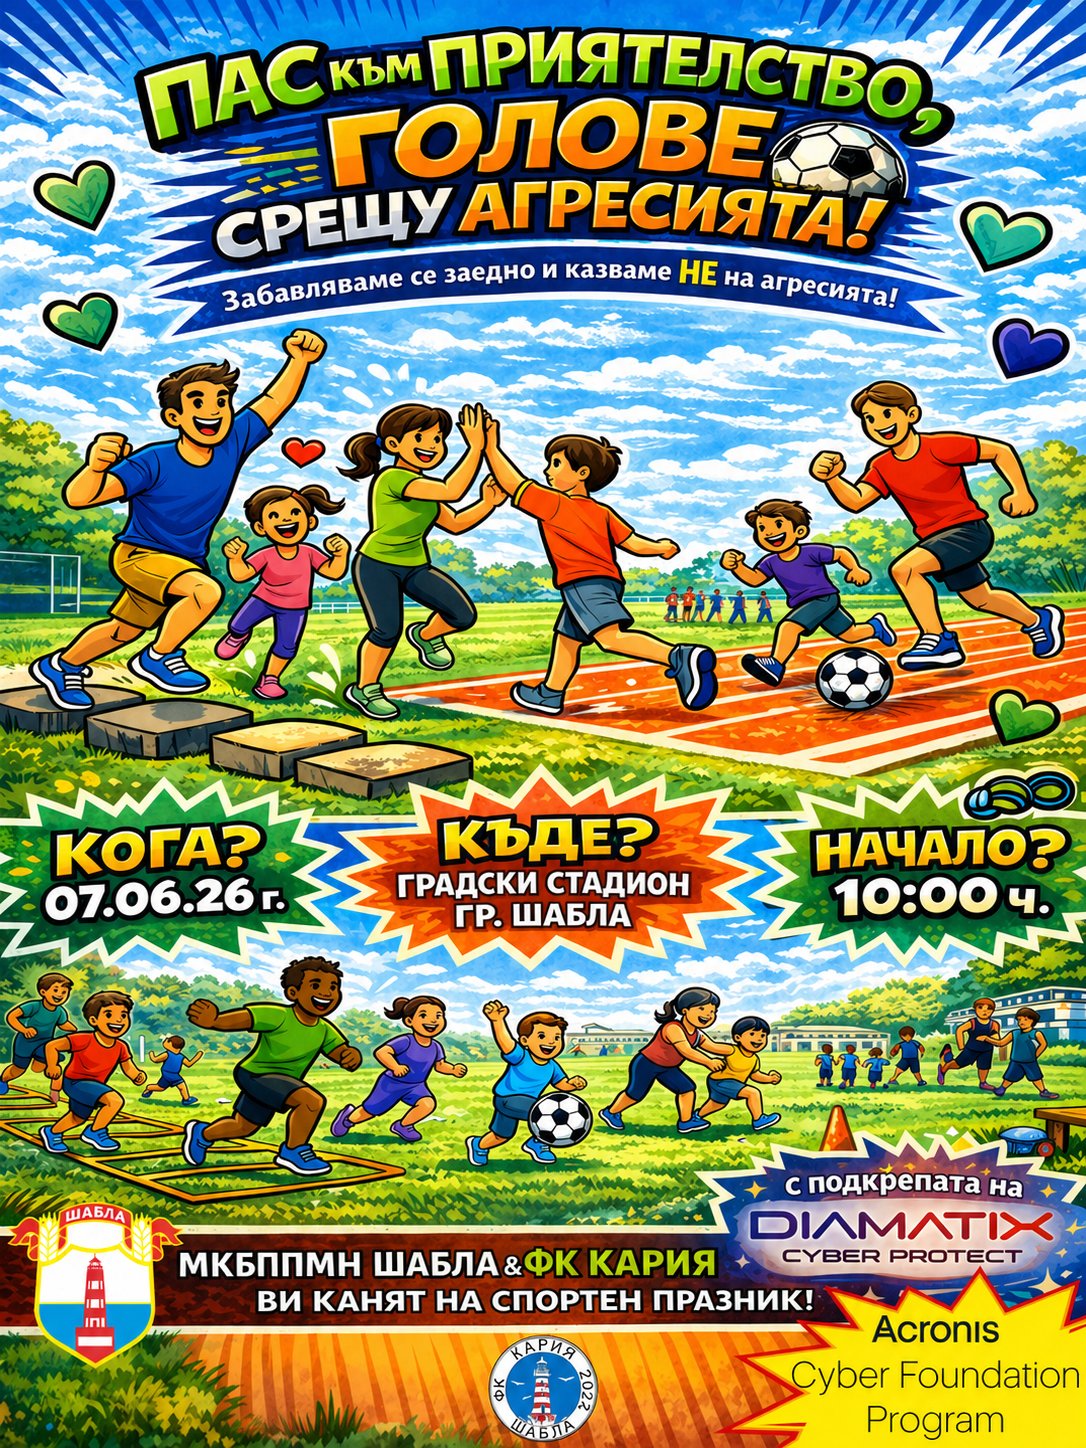
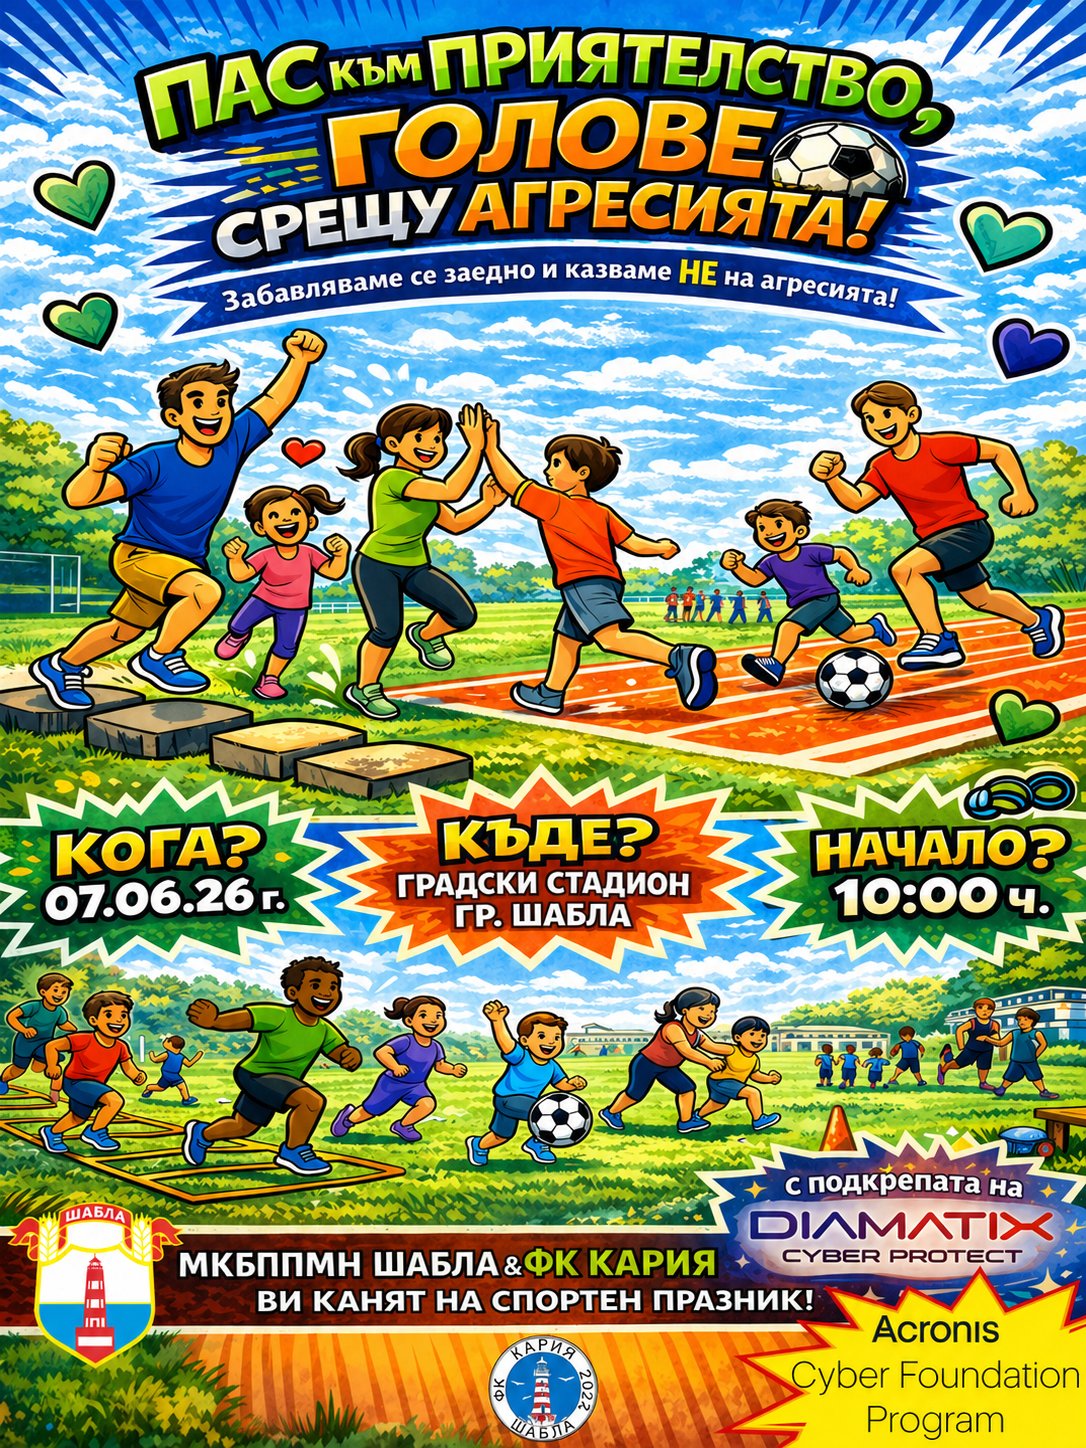
More Than Football: Shabla Brings Children, Families, and Community Together
More Than Football: Shabla Brings Children, Families, and Community Together DIAMATIX Community Shield and Acronis Cyber Foundation Program Supported “Pass to Friendship, Goals Against Aggression” in Shabla On June 7, Shabla hosted the “Pass to Friendship, Goals Against Aggression” initiative, organized by FC Karia…
The Role of Monitoring and SOC in Operational Resilience
The Role of Monitoring and SOC in Operational Resilience TL;DR Operational resilience depends not only on recovery capabilities, but also on visibility. Organizations cannot respond effectively to disruption if they do not know what is happening across their infrastructure, systems, and…
DIAMATIX Community Shield and Acronis Cyber Foundation Program Support “Pass to Friendship, Goals Against Aggression” Initiative in Shabla
DIAMATIX Community Shield and Acronis Cyber Foundation Program Support “Pass to Friendship, Goals Against Aggression” Initiative in Shabla As part of the DIAMATIX Community Shield initiatives, DIAMATIX continues to support local causes focused on children, education, and community development together with…
DIAMATIX MDRunners Completed Business Run Varna 2026
DIAMATIX MDRunners Completed Business Run Varna 2026 The DIAMATIX team took part in Business Run Varna 2026 this Saturday, joining one of the largest corporate relay running events in Bulgaria together with dozens of other company teams from across the region….
MSP Insights Why Clients Buy Response, Not Monitoring TL;DR Most organizations already understand the value of monitoring and visibility. What they increasingly evaluate is how security response actually works during real incidents. Clients look beyond dashboards and alerts. They assess how…
DIAMATIX to Participate in Business Run Varna 2026
DIAMATIX to Participate in Business Run Varna 2026 This Saturday, May 16, 2026, the DIAMATIX team will take part in Business Run Varna, with the start scheduled for 9:00 AM in Varna. Business Run is the largest corporate team-building running event…
World Password Day: Why Strong Passwords Are Not Enough
World Password Day: Why Strong Passwords Are Not Enough Passwords are still the first line of defense. But most modern attacks do not try to “break” them. They simply use them. For years, organizations focused heavily on password complexity policies. Minimum…
Business Impact Analysis (BIA): Defining Recovery Priorities Before Disruption Happens
Business Impact Analysis (BIA): Defining Recovery Priorities Before Disruption Happens TL;DR Not every system requires the same level of protection. When disruption occurs, organizations must know which services need immediate recovery, which processes can tolerate delay, and where operational downtime creates…
DIAMATIX MDR 360° Powered by DIAMATIX SOC Now Available on interworks.cloud Marketplace
DIAMATIX MDR 360° Powered by DIAMATIX SOC Now Available on interworks.cloud Marketplace Managed service providers are expected to deliver more than infrastructure support, endpoint protection, or backup services. Customers expect continuous cybersecurity operations, clear accountability, and confidence that incidents will be…
MSP Insights What Actually Breaks MSP Incident Response And Why Most Security Models Still Miss It Over the past weeks, we’ve looked at several recurring problems inside MSP security operations. Why escalation slows down between detection and action. Why incident response…
The MSP Response Authority Problem: Why Knowing What to Do Doesn’t Mean You Can Act
MSP Insights The MSP Response Authority Problem Why Knowing What to Do Doesn’t Mean You Can Act Security monitoring across MSP environments has improved significantly. Detection is faster. Visibility is broader. Alerts are more accurate. In many cases, teams know what…
LLM SECURITY 101 — Special Edition: When AI Stops Being a Tool and Starts Shaping Judgment
LLM SECURITY 101 — Special Edition When AI Stops Being a Tool and Starts Shaping Judgment AI tools are not just productivity assistants, they are increasingly part of how people think, decide, and cope with complex situations. Over the past year,…
Backup Strategies That Actually Support Disaster Recovery
Backup Strategies That Actually Support Disaster Recovery TL;DR Backup protects data, but not every backup supports recovery. In modern infrastructures, the ability to restore data is only useful if it aligns with how systems are recovered and services are resumed. Effective…
MSP Incident Response Flow Framework Security incidents are detected quickly in most MSP environments. Response is where delays appear. This framework helps structure incident response from detection to action by defining clear stages, responsibilities, and decision points. It is designed to…
AI Security for Everyday Work — a short resource for teams
AI Security for Everyday Work — a short resource for teams AI is already part of everyday work across organizations. It is used for writing, analysis, research, and automation.In most cases, the risk does not come from the tools themselves, but…
The Decision Latency Problem. Why Incident Response Slows Down Even When Everything Is Clear
MSP Insights The Decision Latency Problem Why Incident Response Slows Down Even When Everything Is Clear Across most MSP environments today, detection is no longer the limiting factor. Alerts are generated quickly, correlation works reliably, and in many cases the initial…
The MSP Escalation Problem. Why Response Breaks Between Detection and Action
MSP Insights The MSP Escalation Problem Why Response Breaks Between Detection and Action Security monitoring has improved significantly across MSP environments. Detection technologies are more accurate, visibility is broader, and alerting systems are more sophisticated than ever before. Most MSPs today…
LLM Security 101 Practical Guide . Responsible AI Use in Organizations
LLM Security 101 Practical Guide . Responsible AI Use in Organizations From awareness to safe, practical AI use in everyday work As AI tools become part of everyday workflows, organizations are increasingly facing risks not from the technology itself, but from…
MSP Incident Response Authority Map A Practical Checklist for Defining Operational Security Ownership Security incidents expose operational gaps very quickly. During escalation, many MSP teams discover that responsibilities between monitoring, response, vendor platforms, and client environments are not clearly defined. Questions…
How Disaster Recovery Works: The Systems Behind Operational Resilience
How Disaster Recovery Works: The Systems Behind Operational Resilience TL;DR Operational disruptions don’t happen exactly where organizations expect them. Recent geopolitical tensions and infrastructure disruptions have reminded organizations that operational interruptions can originate outside their own networks. When disruption occurs, the…
DIAMATIX Community SHIELD: Our Team Takes Part in Voluntary Blood Donation
DIAMATIX Team Takes Part in Voluntary Blood Donation A Small Action With Real Impact This week, several members of the DIAMATIX team took time to donate blood at a local transfusion center. Blood donation remains one of the simplest ways individuals…
Who Actually Runs Security at 3AM? The Operational Reality Behind MSP Security Services
MSP Insights Who Actually Runs Security at 3AM? The Operational Reality Behind MSP Security Services Security services are often described through tools and capabilities. Dashboards, alerts, monitoring coverage, automated detection. These elements are important, but they rarely define how security behaves…
When Infrastructure Disruptions Happen: Why Business Continuity Planning Matters
When Infrastructure Disruptions Happen: Why Business Continuity Planning Matters TL;DR Geopolitical tensions and large-scale cyber activity are increasingly affecting digital infrastructure. Disruptions do not always originate inside an organization.Connectivity failures, data center outages, or large-scale DDoS campaigns can interrupt services even…
From Alerts to Ownership: Why MSP Security Models Break Under Real Incidents
MSP Insights From Alerts to Ownership Why MSP Security Models Break Under Real Incidents Most MSP security models don’t break during sales conversations. They break during real incidents. Not because tools fail.But because ownership becomes unclear. In normal operations, alerts look…
NIS2 in Bulgaria: What the 2026 Amendments to the Cybersecurity Act Mean
NIS2 in Bulgaria: What the 2026 Amendments to the Cybersecurity Act Mean NIS2 is not a technological regulation. It is a regulation of governance accountability. TL;DR Change What It Means NIS2 is implemented through amendments to the Cybersecurity Act The requirements…
Compliance-to-Operations Mapping Guide for MSPs Aligning security delivery with NIS2, DORA, ISO 27001 and similar regulatory expectations Regulatory pressure is increasing across industries.For MSPs, compliance is no longer a separate conversation. It directly affects how monitoring, response, documentation, and reporting are…
When Compliance Starts Asking Operational Questions
MSP Insights When Compliance Starts Asking Operational Questions What NIS2, ISO 27001, DORA, and GDPR Change for MSP Security Delivery Models Regulatory frameworks rarely introduce new risks.They make existing ones visible. This is what is currently happening across multiple compliance regimes,…
LLM SECURITY 101 — PART 3: From Awareness to Responsible AI Use
LLM SECURITY 101 — PART 3 From Awareness to Responsible AI Use AI tools are part of everyday workflows, decisions, and automation across organizations. After exploring the fundamentals in Part 1 and the more advanced technical risks in Part 2, this final…
Build vs. Partner: A Practical Decision Framework Scaling security is rarely blocked by technology.It is limited by operating models. As MSPs grow, security delivery becomes harder to sustain.Response expectations increase.Operational load accumulates.Compliance requirements expand alongside customer environments. This framework is designed…
Build vs. Partner: How MSPs Scale Security Without Breaking Their Operating Model
MSP Insights Build vs Partner How MSPs Scale Security Without Breaking Their Operating Model Executive summary Many MSPs reach a point where security demand starts to outgrow their operating model. Not because they lack tools.Not because they lack intent. But because…
DIAMATIX & Acronis: MDR 360° in Practice – Live Demo Webinar for MSPs
DIAMATIX & Acronis: MDR 360° in Practice – Live Demo Webinar for MSPs DIAMATIX, in collaboration with Acronis, is hosting a live demo webinar focused on how Managed Detection and Response (MDR) operates in real MSP environments. The session will provide…
Architects of Chaos. The Most Influential Cybercrime Groups of 2025 and Key Business Lessons
Architects of Chaos The Most Influential and Inventive Cybercrime Groups of 2025 – and What Business Can Learn from Them When we talk about cybersecurity, we often focus on tools, platforms, and controls. But behind most large-scale cyber incidents are not…
MSP Security Operating Model Checklist Security pressure on MSPs doesn’t come from a single place.It builds up through response expectations, operational load, and growing compliance demands. This checklist is designed as a practical self-check.It helps MSPs reflect on how security is…
The MSP Security Reset What Is Already Changing. And What MSPs Must Adapt To Cybersecurity for MSPs has crossed a threshold. This isn’t about what might happen “next”. It’s about what is already visible across customer environments. Attack techniques, regulatory expectations,…
Welcome to MSP Insights MSP Insights is a curated space for observations drawn from real security operations in managed environments. Here we focus on how security behaves under pressure — at scale, across multiple customers, and under growing regulatory expectations. The…
Welcome to Practical Resources for MSPs This section contains practical materials created to support day-to-day security operations in MSP environments. Here you will find working documents such as checklists, diagrams, reference guides, and decision-support materials covering topics like SOC operations, MDR…
LLM SECURITY 101 — PART 2: Advanced Risks and Practical Safeguards for Everyday AI Use
LLM SECURITY 101 — PART 2 Advanced Risks and Practical Safeguards for Everyday AI Use As AI tools become more deeply embedded in daily business workflows, the conversation naturally moves beyond basic usage and early mistakes.Organizations are no longer asking whether…
Holiday Cyber Risk: Why Reduced Coverage Is the Real Threat
Holiday Cyber Risk: Why Reduced Coverage Is the Real Threat The holiday season is often associated with lower business activity, lighter workloads and slower decision-making.From a cybersecurity perspective, however, this period represents one of the most predictable risk windows of the…
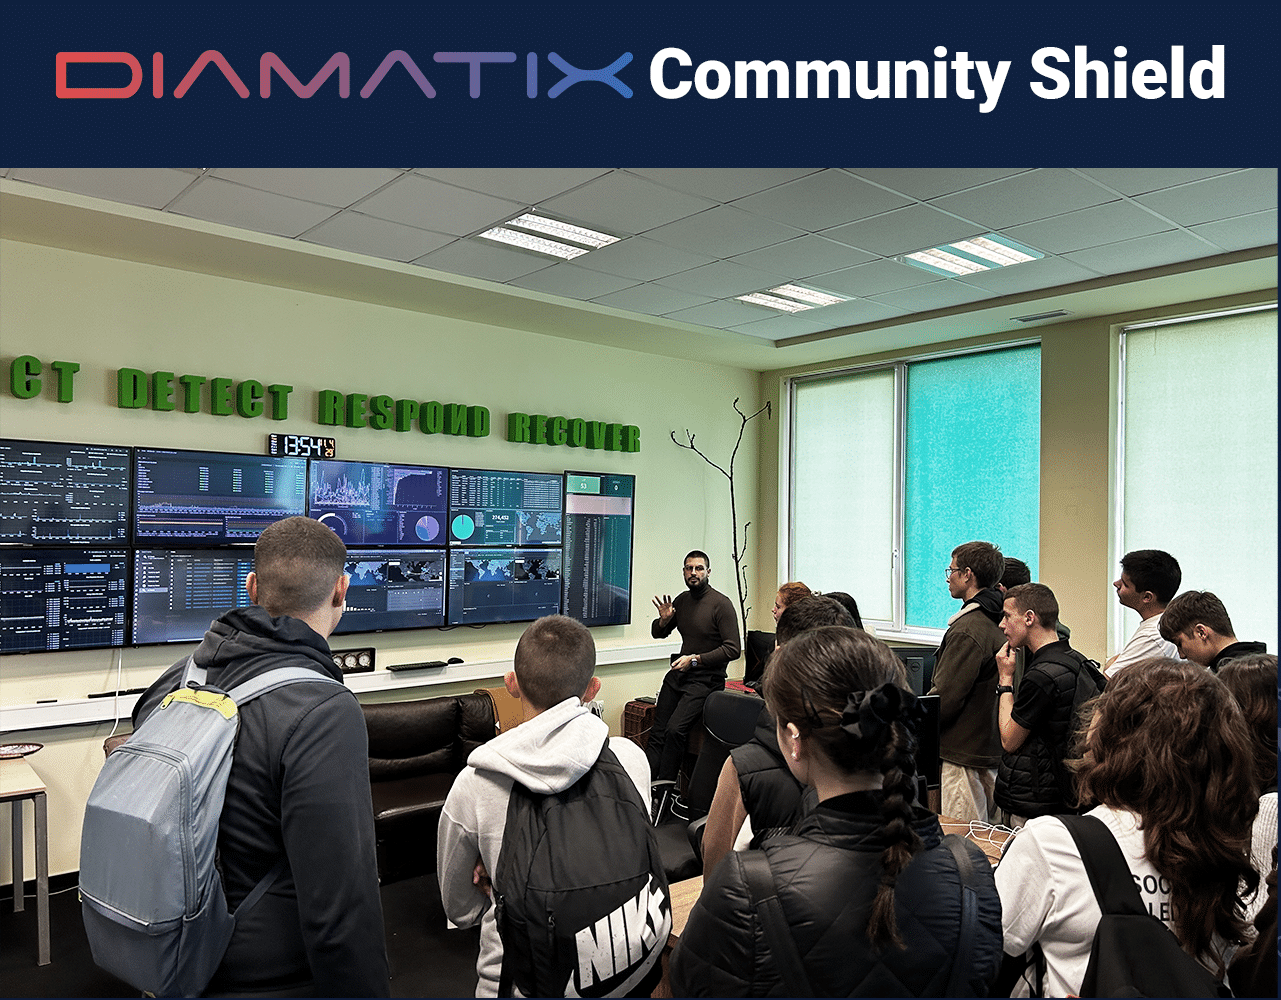
DIAMATIX Community Shield: Logic, Math & Cyber — A Visit with Grade 10B (Mathematics) from St. Stefan Karadzha – Kavarna
DIAMATIX Community Shield: Logic, Math & Cyber — A Visit with Grade 10B (Mathematics) from St. Stefan Karadzha – Kavarna In December We welcomed Grade 10B (Mathematics track) from St. Stefan Karadzha Secondary School to our office for a session on…
LLM SECURITY 101 — PART 1: Understanding the Basics & Key Early Risks
LLM SECURITY 101 — PART 1 Understanding the Basics & Key Early Risks As we prepare for 2026, AI tools — especially large language models (LLMs) — are becoming part of everyday work. December is a good moment to focus on…
What NIS2 Audits Will Look Like in 2026 — and How Organizations Can Prepare Today
What NIS2 Audits Will Look Like in 2026 — and How Organizations Can Prepare Today NIS2 is entering a decisive phase. After the completion of national transpositions across the EU in 2025, Member States are now preparing for the first official…
Leadership and Vision Behind the D-NAVIO Consortium
Leadership and Vision Behind the D-NAVIO Consortium Inside Horizon Europe D-NAVIO: Challenges and Opportunities in Coordinating a Multi-Country Consortium At the heart of every ambitious European research project stands not only innovation but also collaboration — the ability to unite expertise,…
Cyber Resilience in the Age of the Digital Euro What it means and why it matters for your compliance strategy The evolution of digital payments has reached a critical milestone in Europe. The European Central Bank (ECB) is preparing for a…
DIAMATIX Community Shield initiative: Entrepreneurship & Cyber Defense Up Close with Grade 10A from St. Stefan Karadzha School – Kavarna
DIAMATIX CommunityShield: Entrepreneurship & Cyber Defense Up Close with Grade 10A from St. Stefan Karadzha – Kavarna On Nov 4, 2025, we hosted Grade 10A (Entrepreneurship track) at the DIAMATIX office — a conversation about courage to start, lessons learned, and…
ISO 27001, NIS2, DORA and GDPR: Mapping the EU Cybersecurity Landscape
ISO 27001, NIS2, DORA and GDPR: Mapping the EU Cybersecurity Landscape European organizations are entering a new era of cybersecurity governance. Regulations such as NIS2 and DORA are now active, while GDPR remains the benchmark for data protection — and ISO…
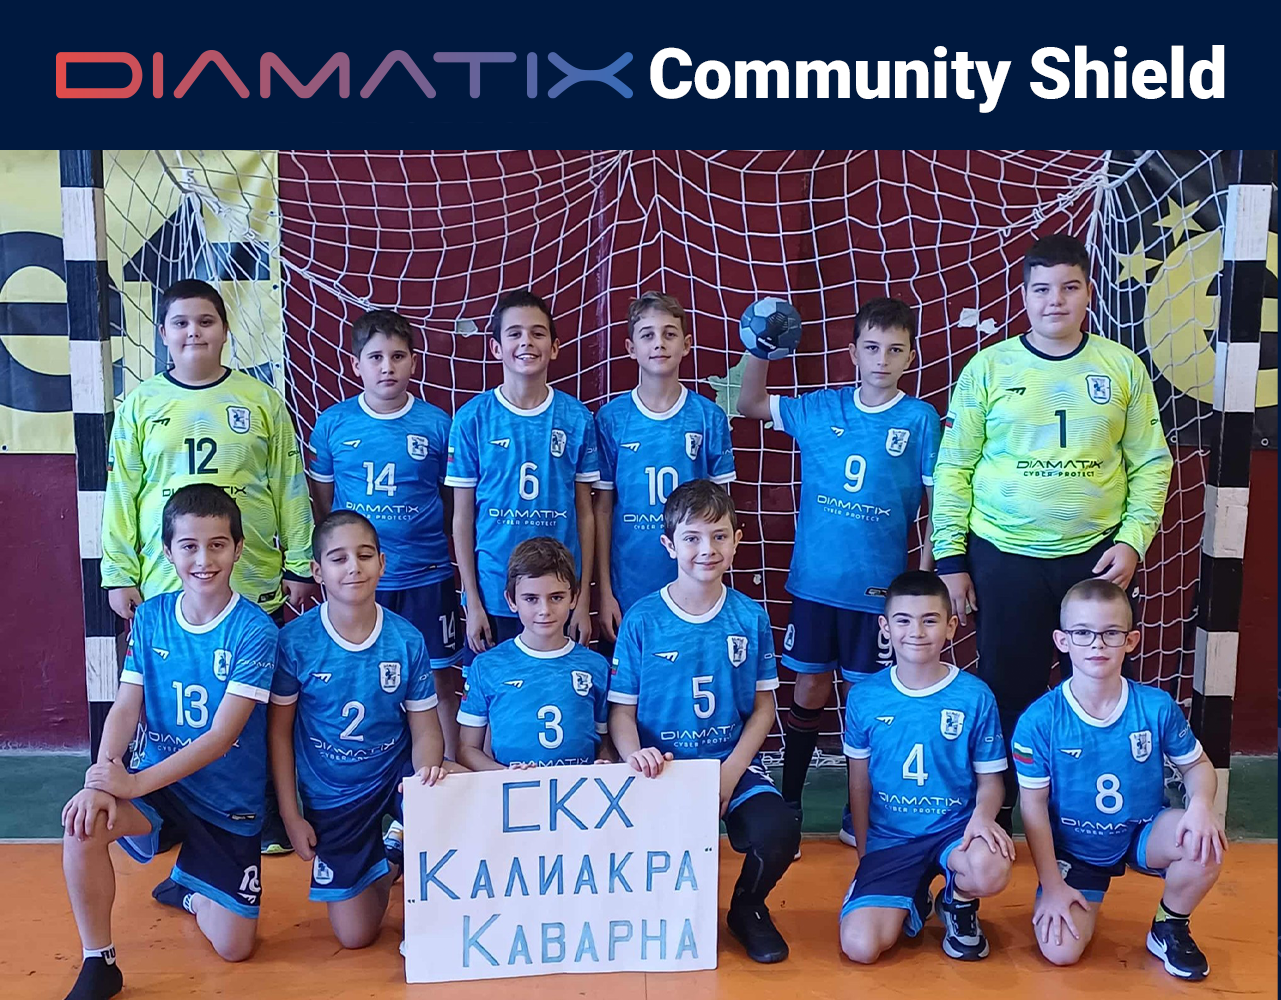
DIAMATIX supports the young athletes of Kaliakra Handball Club – Kavarna
DIAMATIX supports the young athletes of Kaliakra Handball Club – Kavarna As part of our DIAMATIX Community Shield program, we’re proud to stand behind young athletes who embody teamwork, discipline, and perseverance. What happened: DIAMATIX supported the Kaliakra Handball Club –…
ISO 27001, NIS2 and DORA: Choosing What Comes First
ISO 27001, NIS2 and DORA: Choosing What Comes First Across Europe, cybersecurity compliance has become a multi-layered challenge. Organizations now face three major frameworks — ISO/IEC 27001, NIS2, and DORA — each setting new expectations for how risk, resilience, and information…
What is NGFW and How It Supports NIS2 and DORA Compliance
What is NGFW and How It Supports NIS2 and DORA Compliance Firewalls have long been the foundation of network defense. But in today’s world of encrypted traffic, SaaS applications, and sophisticated cyber threats, traditional firewalls are no longer enough.Enter the Next-Generation…
DORA vs NIS2: Key Differences and What They Mean for Your Organization
DORA vs NIS2: Key Differences and What They Mean for Your Organization In the evolving landscape of EU cybersecurity regulations, two major frameworks stand out: the NIS2 Directive and the DORA Regulation.While both aim to strengthen the resilience of critical sectors,…
DIAMATIX Achieves Acronis Platinum Partner Status: What It Means for Our Clients
DIAMATIX Achieves Acronis Platinum Partner Status: What It Means for Our Clients Last week, DIAMATIX was officially recognized as a Platinum Partner in the Acronis #CyberFit Partner Program – the highest level of trust and expertise within the Acronis ecosystem. But what does…
Single Point of Failure: When One Weak Link Cripples Critical Infrastructure
Single Point of Failure: When One Weak Link Cripples Critical Infrastructure In today’s hyper-connected world, the resilience of critical infrastructure often depends on a single platform, vendor, or system. When that single point fails, the result can be a domino effect…
EU Data Act Enters into Force: What It Means for Business
EU Data Act Enters into Force: What It Means for Business September 2025 – The EU Data Act (Regulation (EU) 2023/2854) officially came into effect on 11 January 2024. Most of its provisions, however, become applicable as of 12 September 2025,…
DIAMATIX as part of Horizon Europe D-NAVIO: advancing Intelligent Digital Twins for safer, smarter shipping
DIAMATIX as part of Horizon Europe D-NAVIO: advancing Intelligent Digital Twins for safer, smarter shipping As part of the Horizon Europe project D-NAVIO (Digital-Ship), DIAMATIX contributes cybersecurity and compliance expertise to the development of next-generation Intelligent Digital Twins (IDT) for large vessels. Coordinated by…
MDR for Smart Factories: NIS2-Ready Detection & Response in the Era of Industry 4.0
MDR for Smart Factories: NIS2-Ready Detection & Response in the Era of Industry 4.0 Manufacturing: The Most Targeted Industry in 2024–2025 The manufacturing industry is undergoing a profound transformation. The shift towards Industry 4.0 is connecting operational technology (OT) with traditional…
MDR ROI & Vendor Checklist How to measure the real business value of Managed Detection & Response— and pick a partner who can deliver it 1. Why talk about “return” at all? Attackers count dwell-time in hours; boards count losses in…
NIS2 Readiness: 24×7 MDR Guide for CISOs How always-on Managed Detection & Response shrinks risk and speeds compliance. 1. Why NIS2 Raises the Stakes for Critical Sectors The NIS2 Directive expands its scope to thousands of “essential” and “important” entities and…
SHIELD: The Leader in Comprehensive Security for SMEs
Running a business today is like driving a Formula 1 car on a track filled with potholes. You’re moving fast, competition is tight, and out of nowhere – boom – a security threat pops up. That phishing email. That compliance red…
2024 in Review: DIAMATIX’s Breakthroughs in Cybersecurity and Innovation
As we step into 2025, the past year at DIAMATIX was defined by transformation and innovation. With businesses facing growing cybersecurity challenges, including the EU’s stringent NIS2 Directive, we focused on empowering organizations to not only stay secure but also thrive…
A Refreshed Cyber Resilience Plan Can Help Your Business in Three Significant Ways
Shoring up both your cyber defenses and recovery capabilities will improve your company’s posture with IT regulators, cybersecurity standards bodies, and insurers. Recent cybersecurity research reveals unwelcome news for businesses striving to manage their operational risk in a world where cybercriminals…
Cybersecurity in Healthcare: NIS2 Compliance Is No Longer Optional
The healthcare sector has long been a target for cybercriminals, and the consequences of a cyberattack in this industry are more severe than in many others. From hospitals and clinics to medical device manufacturers and insurers, healthcare organizations store and manage…
Cybersecurity in Q4 2024: Trends, Threats, and Triumphs
As we close out 2024, the cybersecurity battleground is anything but quiet. Emerging threats push boundaries, while innovation continues to redefine how we protect our digital spaces. From ransomware’s relentless grip to AI’s dual-edged capabilities, let’s unpack the key trends shaping…
The NIS2 Directive (Network and Information Security Directive 2) is a European Union legislative framework aimed at improving cybersecurity across various sectors, particularly in essential and important entities like financial services, healthcare, energy, and telecommunications. Non-compliance with this directive can have…
How Cybersecurity Budgets Will Change with NIS2: What to Expect and How to Prepare
With the enforcement of the NIS2 Directive approaching, many businesses are grappling with the potential financial impact of compliance. The directive significantly expands the range of industries and businesses required to adhere to stringent cybersecurity measures, meaning that companies of all…
How to Leverage NIS2 Compliance for Competitive Advantage
Leveraging NIS2 compliance for competitive advantage involves turning regulatory requirements into opportunities for growth, reputation enhancement, and operational resilience. The NIS2 Directive, aimed at strengthening cybersecurity across the EU, goes beyond just a legal obligation—it offers businesses significant strategic benefits. 1….
The Network and Information Security (NIS) Directive, adopted in 2016, was the first EU-wide legislation aimed at improving cybersecurity across the member states. It required essential service providers in sectors like energy, healthcare, and transport to implement cybersecurity measures and report…
NIS2 and Digital Transformation: Securing the Future of Cyber Resilience
Digital transformation is reshaping industries globally, driving efficiency, innovation, and growth. However, as organizations increasingly rely on digital technologies, the risk of cyber threats also escalates. In response to this, the European Union has introduced the Network and Information Systems Directive…
ABC Wind Farm Strengthens Renewable Energy Operations with DIAMATIX
ABC Wind Farm, part of Long Man Holding Wind Energy, is a Bulgarian renewable energy company focused on the development, operation and management of wind farm projects. The company supports critical renewable energy infrastructure where secure systems, reliable data protection and operational continuity are essential.
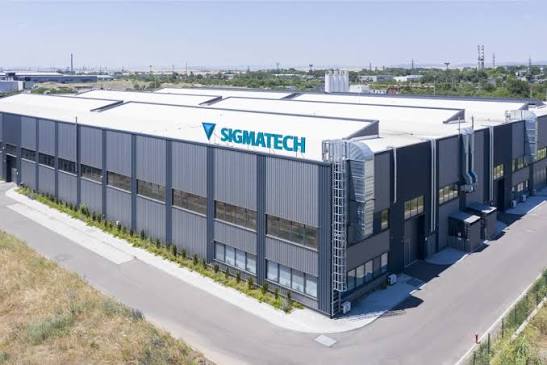
SIGMATECH Builds Compliance-Ready Security with DIAMATIX
SIGMATECH Ltd., together with its subsidiary LLC Paton Turbine Technologies, is a high-tech research and production company specializing in aircraft and industrial gas turbine engine components. Its core expertise includes thermal-resistant and thermal barrier coatings, as well as rejuvenation of hot-section turbine parts.
Unimasters Strengthens Operational Resilience with DIAMATIX
Unimasters is a leader in logistics and supply chain management, providing land, sea and air transport solutions, cargo management, 3PL/4PL services and e-commerce logistics. Its operations depend on reliable infrastructure, secure access, protected data and uninterrupted services.
BULPHARMA Improves Response Time and Visibility with MDR 360° powered by DIAMATIX SOC
BULPHARMA is one of Bulgaria’s leading healthcare and pharmaceutical groups, operating multiple hospitals and outpatient facilities across the country. Its distributed healthcare infrastructure supports more than 1,600 endpoints, 35+ servers, and critical medical systems where uninterrupted availability is essential for patient care.