DIAMATIX SOC · Since 2019
Our SOC is our core business
Since 2019, the DIAMATIX Security Operations Center has been the operational engine behind MDR360 and every managed security service we deliver — monitoring, investigating and responding to threats around the clock.
Why it matters
Security operations is what we do — every day, every night
Many providers add a SOC to a wider IT portfolio. For DIAMATIX it is the centre of the company. Since 2019 we have built our people, processes and SHIELD platform around one goal: making sure that when an alert matters, someone qualified investigates it and acts on it.
- Operating since 2019 as a dedicated European SecOps and Incident Response company
- 24/7/365 monitoring, triage and escalation
- Analysts, incident responders and detection engineers in one team
- The same SOC delivers MDR360 to direct clients and MSP partners
How the SOC works
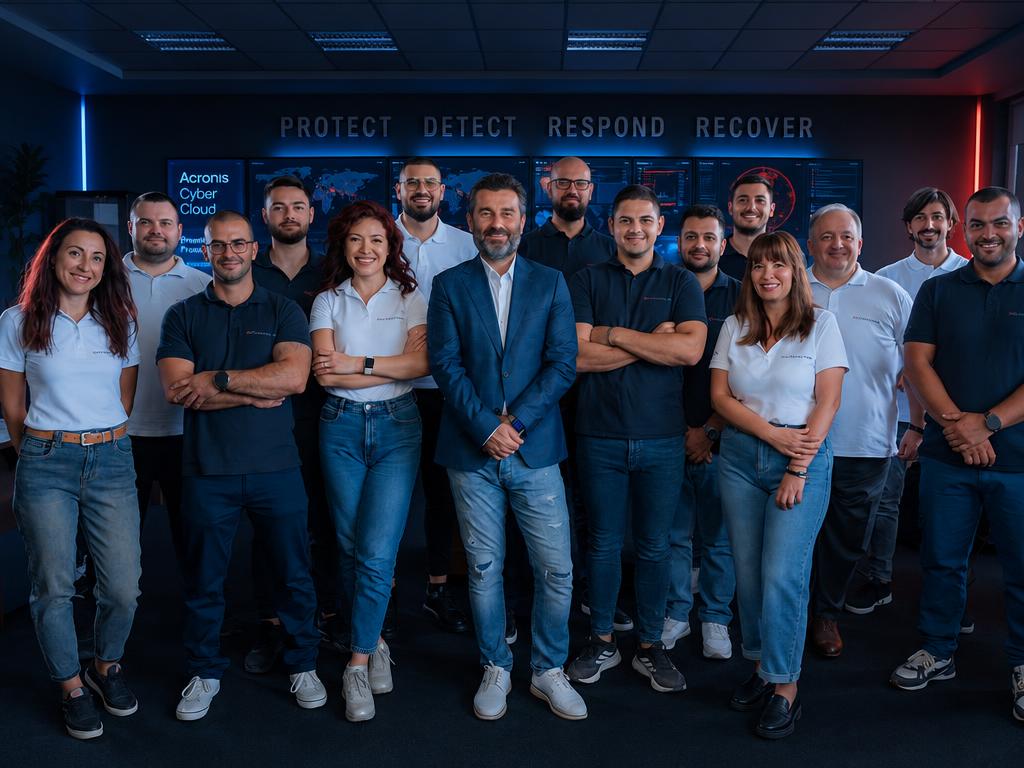
Three foundations
People
Security analysts and incident responders working in shifts to provide continuous coverage, supported by detection engineers who tune rules for each environment.
Process
Documented triage, escalation and response playbooks with clear severity levels, agreed contacts and approved response permissions.
Platform
SHIELD SIEM/XDR correlates telemetry from customers' existing security technologies into a single investigation view.
From signal to outcome
How every alert is handled
A consistent path from the first signal to a documented outcome.
- 01
Collect
Telemetry from endpoints, identities, email, cloud and network tools flows into SHIELD.
- 02
Correlate
Detections are enriched and correlated to separate real threats from noise.
- 03
Investigate
An analyst reviews every escalated alert, establishes scope and assigns severity.
- 04
Respond
You are notified, and containment actions are taken within your approved permissions.
- 05
Report
Each incident is documented with findings, actions taken and recommendations.
Incident response
When it is a real incident, you are not alone
Detection is only half the job. Our incident responders work alongside your team to contain the threat, understand what happened and get operations back on track — with clear communication at every step.
- Every escalated alert is reviewed by an analyst
- Response actions stay within your approved permissions
- Clear, documented communication for each incident
- Post-incident findings and hardening recommendations
What the SOC delivers
Capabilities behind every service
Continuous monitoring
Round-the-clock visibility across the technologies you already use.
Threat detection & hunting
Correlation rules and analyst-led investigation to find threats tools alone miss.
Defined response times
Severity-based response commitments aligned with the MDR360 service levels.
Reporting
Incident reports and regular service reporting through the customer portal.
Continuous tuning
Detections are refined over time to reduce noise and focus on what matters.
European operations
European-based operations and data handling for organisations with regulatory obligations.
FAQ
About the DIAMATIX SOC
Meet the SOC behind MDR360
Arrange a consultation and see how our analysts would work with your environment.