DFARS readiness
Connect applicable contractual cyber requirements to incident escalation, evidence preservation and reporting workflows. Agree who owns notifications and which information can be shared before an incident occurs.
DIAMATIX · MDR360
Protect sensitive engineering data, supplier connections and production continuity with MDR360. DIAMATIX brings experience with DFARS and NIST frameworks for defense companies, connecting security requirements to day-to-day detection and response.
Discuss Defense Security & MDR360DIAMATIX · MDR360
For defense manufacturers, engineering businesses and their suppliers, requirements need to translate into working controls. Shape the engagement around your contractual obligations, sensitive information and existing security stack.
Connect applicable contractual cyber requirements to incident escalation, evidence preservation and reporting workflows. Agree who owns notifications and which information can be shared before an incident occurs.
Where applicable, use NIST SP 800-171 to structure safeguarding of Controlled Unclassified Information (CUI). Scope monitoring, identity visibility and response evidence around the systems that handle it; broader control implementation is separately agreed.
Use NIST CSF 2.0 to connect Govern, Identify and Protect with Detect, Respond and Recover. MDR360 anchors detection and response; separately scoped advisory work can help prioritize gaps across the wider framework.
Prioritize supplier access, privileged accounts and engineering endpoints. Agree containment playbooks that protect sensitive data without assuming production systems can be isolated automatically.
Sector risk
01
02
03
Outcome Plane
Agree the scope, measure the actions and prioritize the next improvements.
DFARS applicability, relevant NIST requirements and permitted data handling depend on your contracts and environment. Telemetry, access, retention, response permissions and escalation are agreed before onboarding. MDR360 supports security operations and evidence; it does not certify compliance or assume access to classified systems.
Identify essential services, assets, supported technologies and dependencies.
Define permissions, escalation contacts and business-safety constraints.
Track coverage, response actions and unresolved exposure.
Customer stories
Case study
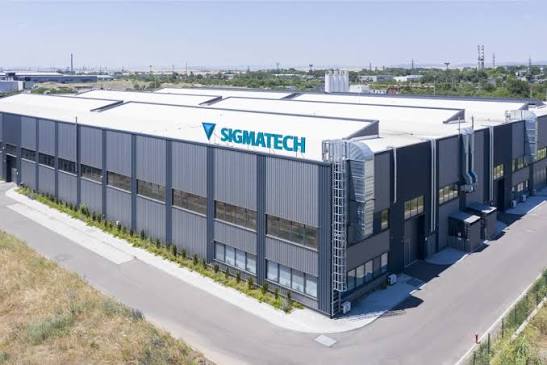
SIGMATECH Ltd., together with its subsidiary LLC Paton Turbine Technologies, is a high-tech research and production company specializing in aircraft and industrial gas turbine engine components. Its core expertise includes thermal-resistant and thermal barrier coatings, as well as rejuvenation of hot-section turbine parts.
Read case study